

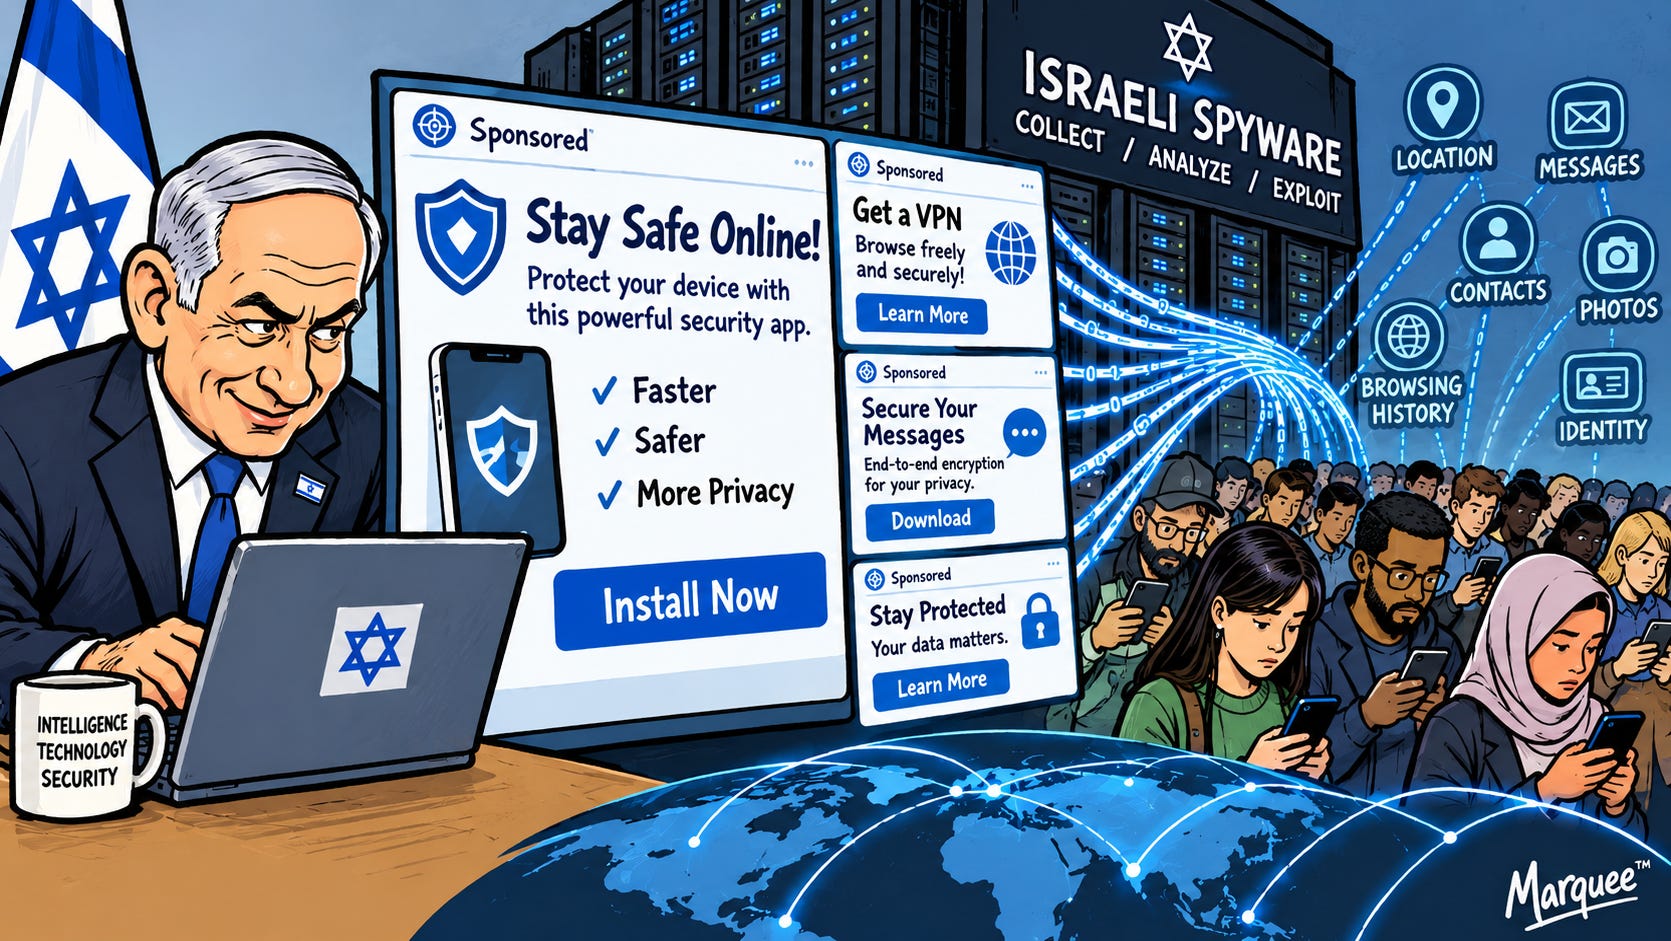
For years, people joked that online ads were creepy — tracking clicks, following you around the internet, profiling your habits. What almost no one imagined was that an ad you never clicked could be the entry point for a military‑grade spyware operation. But that is exactly what investigators uncovered when they traced a sprawling espionage campaign back to an Israeli digital marketing agency called Discover‑Tech.
A joint investigation by Canadian cyber watchdog Citizen Lab and U.S. ad‑security firm Confiant revealed that Discover‑Tech had quietly transformed the global advertising ecosystem into a surveillance pipeline. The company operated across more than 120,000 websites and 75,000 mobile apps, pushing out millions of ads per day. On the surface, these ads looked ordinary. Behind the scenes, they were part of a system designed to identify targets, track their devices, and infect them with spyware — all without a single click.
How the operation worked
The technique Discover‑Tech used is known as AdFection, and it weaponizes the real‑time bidding (RTB) system that powers online advertising. Whenever you open a webpage or app, an ad slot triggers an automated auction. Dozens or hundreds of companies bid to show you an ad. The winning bidder’s code loads instantly.
Discover‑Tech exploited this moment.
When one of their ads loaded, it quietly sent your device details — IP address, browser type, advertising ID — to a server the company controlled. If you weren’t a target, nothing happened. But if you were on their list, the server responded with malicious code hidden inside a tiny, invisible frame. That frame contacted a second server linked to Candiru, an Israeli spyware vendor. If your device passed Candiru’s fingerprinting checks, the exploit server delivered a zero‑click infection chain.
No interaction.
No warning.
Just compromise.
This selective targeting made the operation extremely difficult to detect. Security scanners reviewing the ads saw nothing unusual because the malicious payload only appeared for chosen devices.
📽️ Credit: Sovereign Media
The scale of exposure
Citizen Lab and Confiant found that Discover‑Tech’s infrastructure was massive:
Over 120,000 websites
More than 75,000 mobile apps
Roughly 10 million ads served per day
At least 442 million ads delivered during the period investigators examined
These ads appeared on major platforms — including BBC, The New York Times, Duolingo, Badoo, and Grindr — as well as other news sites, dating apps, language‑learning apps, and entertainment platforms, touching hundreds of millions of people worldwide.
But the real concern wasn’t the reach. It was who the operation focused on.
Who was targeted
Citizen Lab confirmed that at least 45 devices belonging to Al Jazeera staff were compromised. These weren’t random infections — they were deliberate, targeted attacks on journalists.
Confiant’s analysis showed Discover‑Tech’s ads appearing inside networks used by:
The U.S. Department of Defense
The International Atomic Energy Agency (IAEA)
The International Criminal Court (ICC)
The European Commission
National cybersecurity agencies
NATO‑linked networks
Palestinian territories were subjected to particularly dense ad‑placement patterns, indicating focused surveillance in those regions.
The ICC detail is especially notable: the court has issued arrest warrants for Benjamin Netanyahu over war crimes in Gaza. The fact that spyware‑linked ads were circulating inside ICC‑connected networks raises serious geopolitical questions.
The spyware behind the ads
The payload delivered through AdFection came from Candiru, a notorious Israeli mercenary spyware vendor sanctioned by the U.S. government. Candiru’s tools are designed for full device takeover — messages, microphone, camera, files, everything.
Citizen Lab found login records on Discover‑Tech’s systems tied to Candiru employees, confirming operational collaboration.
Candiru recruits heavily from Unit 8200, Israel’s military cyber‑warfare unit. Unit 8200 alumni populate the leadership of multiple Israeli surveillance companies, including NSO Group and Intellexa. Discover‑Tech appears to have been part of this same ecosystem: a civilian‑facing company acting as a delivery mechanism for military‑grade spyware.
Discover‑Tech wasn’t an ad company — it was a spyware broker
Citizen Lab’s deeper analysis showed that Discover‑Tech wasn’t actually selling ads in any meaningful commercial sense. The company recorded 3.77 billion ad bids in four months but zero legitimate sales. Its platform, Controlium, was built not for marketing but for device fingerprinting, de‑anonymization, and targeted infection.
Discover‑Tech served multiple spyware vendors, not just Candiru. It acted as a bridge between the global advertising ecosystem and mercenary cyber‑espionage networks.
The ad system itself — the infrastructure that powers nearly every free website and app — was used as a weapon.
Why this matters
AdFection proves that online advertising isn’t just a privacy problem. It is a security threat. The RTB system broadcasts device identifiers to hundreds of bidders every time an ad loads. Discover‑Tech weaponized this architecture to run espionage operations across continents.
As Citizen Lab researcher Wolfie Christl put it:
“The digital advertising ecosystem is fundamentally broken. It is a security threat for governments, companies, civil society, and ordinary people.”
This investigation shows that the threat isn’t theoretical. It’s already happening.
Your smart phone isn’t safe. Maybe it never was. If you really want to keep the spies out of your pocket, it’s time to go back to the Nokia brick — the indestructible one that does nothing but make calls and play Snake.
Please provide investigation details? Thank you!